

Before you start
- A Team or Enterprise plan on an MCP client that supports Enterprise Managed Auth, with your identity provider connected and admin access to it.
- An Exa organization (not a personal team) with SSO and directory sync, and admin access to it.
- Okta as your identity provider, on Okta Identity Engine with Cross App Access (XAA) enabled, and Super Admin access to the tenant. Okta is the only identity provider supported today.
- Enterprise Managed Auth enabled on your Exa organization. If the Enterprise managed auth section does not appear on your Organization page, ask your Exa contact or support@exa.ai to enable it.
Exa values you’ll need
Set up EMA
1
Provision your members in Exa
Every member who will use the connector must already exist in Exa and belong to a team in your Exa organization, with the same email address Okta asserts, on a domain verified on your organization. EMA never creates accounts. Use directory sync, or invite them to the team.
2
Register your identity provider in Exa
In the Exa dashboard, open Organization, find Enterprise managed auth, and click Register identity provider. Paste the SSO URL of the Exa app in Okta (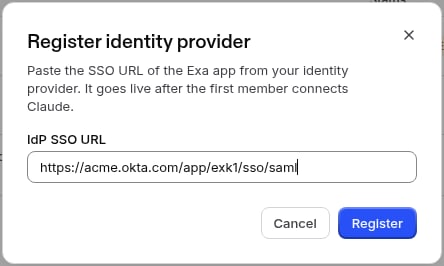
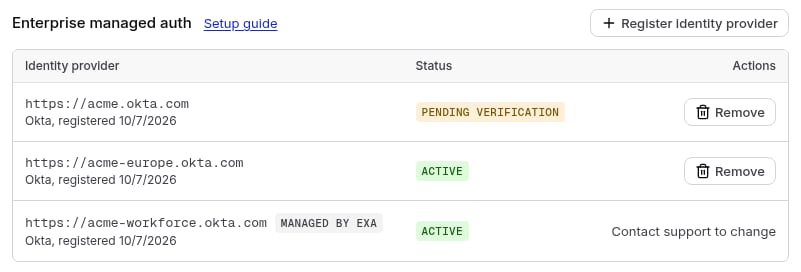
https://your-org.okta.com/app/.../sso/saml). Exa validates the URL and checks your Okta tenant’s signing keys when you register it. Only organization admins can register or remove an identity provider. If your Okta tenant uses a custom domain (https://login.your-company.com/...), send the URL to support@exa.ai instead; Exa registers it for you and it shows as Managed by Exa.3
Configure Cross App Access in Okta
Follow Okta’s AI agent-to-app Cross App Access guide. For Exa:
- Open the Exa application in the Okta Admin Console, go to Resource Server, enable XAA, and set the Resource URL and Issuer URL to
https://auth.exa.ai. Leave Audience/tenant ID empty. - If the Exa app is a custom SAML app, confirm its Name ID Format is
EmailAddress, since Exa matches the asserted email to the member’s Exa account. - Register your MCP client under Directory → AI Agents, add its public key and delegated caller, and add Exa as a Resource Connection using the Client ID your MCP client vendor provides.
4
Turn on managed authorization in your MCP client
In your MCP client’s organization settings, open the Exa connector and enable managed authorization. Confirm the IdP connection, run the test, choose the roles that inherit the connector, and save. For example, see Anthropic’s admin guide for Claude’s role and scope options.
Usage through Enterprise Managed Auth bills to the member’s Exa team, under that team’s plan and rate limits, the same as anything else they run on the team.
Revoking access
- One member: remove them in Okta, or from their team in Exa. Either one ends their managed MCP access.
- Everyone: remove the issuer on the Organization page, or turn managed authorization off in your MCP client. New connections stop immediately and sessions already open end shortly after. You can register the issuer again at any time.
Troubleshooting
It works for some members but not others
It works for some members but not others
The failing member isn’t resolvable in Exa. Check that they exist in Exa with the exact email Okta asserts, on a domain verified on your organization, and that they belong to a team in that organization. A directory sync group mapping is the usual culprit.
Nothing works for anyone
Nothing works for anyone
Check the issuer’s status on the Organization page. Still Pending verification means no connection has succeeded yet. Usually the Okta configuration isn’t finished, the Issuer URL on the Exa app doesn’t match
https://auth.exa.ai, or the member who tried isn’t provisioned in Exa. Fix that, then connect again as a provisioned member.Registration says the identity provider is already registered
Registration says the identity provider is already registered
An issuer belongs to exactly one Exa organization. If it isn’t listed on your Organization page, contact support@exa.ai.
For anything else, contact support@exa.ai with your Exa organization name, the affected member’s email, and roughly when the attempt happened.